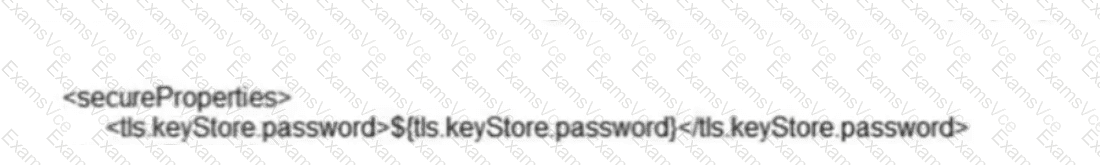
The Mule Maven Plugin's CloudHub 2.0 deployment configuration supports a top-level < secureProperties > element. Properties supplied through this element are treated differently from ordinary deployment properties: CloudHub 2.0 encrypts their values before storing them.
MuleSoft's deployment documentation explicitly states that < secureProperties > is used to set application properties and instruct CloudHub 2.0 to encrypt the values before storing them. This is particularly appropriate for TLS credentials such as keystore passwords because these values should not be persisted as ordinary clear-text application configuration.
The important distinction is between encryption and UI masking. A masked field merely hides its visual representation; it does not by itself establish protected storage. In CloudHub 2.0, protected property values are stored securely and are not retrievable as plain values through Runtime Manager. Anypoint Studio is also not the component responsible for protecting a value supplied through the CloudHub deployment configuration, nor is this deferred to the Mule application's runtime flow.
Therefore, with the property placed under the Mule Maven Plugin's < secureProperties > configuration, CloudHub encrypts the value.
Reference topics: CloudHub 2.0 deployment; Mule Maven Plugin; secure properties; protected application configuration.
Official documentation: https://docs.mulesoft.com/mule-runtime/4.6/deploy-to-cloudhub-2
Official documentation: https://docs.mulesoft.com/cloudhub-2/ch2-protect-app-props
===============================================================