Order
Action
1
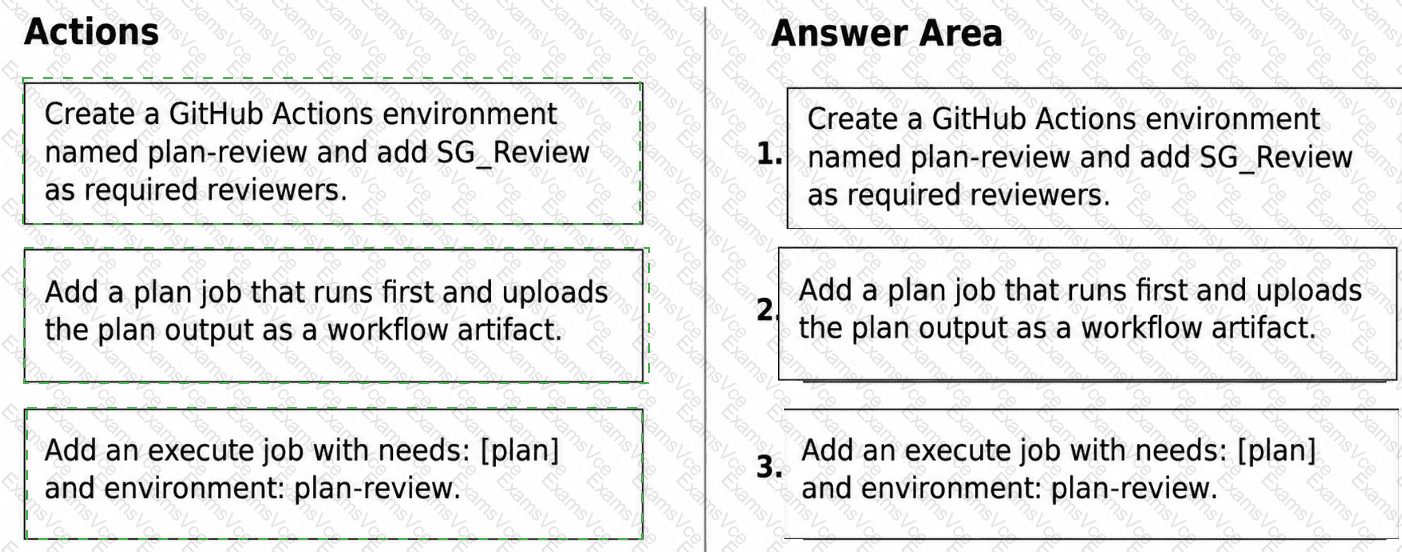
In the product-api repository settings, create a GitHub Actions environment named plan-review and add SG_Review as the required reviewers.
2
To the agent1 workflow, add a plan job that runs first and uploads the plan output as a workflow artifact.
3
Add an execute job that has needs: [plan] and environment: plan-review.
The review environment must exist before a workflow job can reference it. Required reviewers on plan-review establish the approval gate that protects execution of the agent’s proposed plan.
The workflow then requires a plan job that runs before execution and uploads the plan as an artifact. This creates a durable review object rather than requiring reviewers to approve an undocumented or transient agent decision. The artifact is available for inspection during the approval stage and for later audit.
Finally, the execute job declares needs: [plan] to enforce sequencing and targets the plan-review environment. When that job reaches the protected environment, required reviewers must approve it before the protected execution can proceed. This creates a contro lled sequence: generate evidence, review evidence, then authorize execution.
Branch-protection rules and automatic advancement are not substitutes for environment-based approval of the execution job.
Study-guide topics: human-in-the-loop approvals, protected environments, artifacts, and staged agent execution.
===============