Comprehensive and Detailed Explanation
HPE Press guide context | PDF page 125 | HPE Press, Aruba Certified Associate – Campus Access Official Certification Study Guide
Technical Deep Dive — Original Chat Wording
The command vlan trunk allowed all configures an AOS-CX trunk to permit traffic associated with all VLANs defined on the switch.
An important characteristic is that the permitted VLAN membership automatically includes subsequently created VLANs.
For example, consider the configuration:
configure terminal
interface 1/1/24
no routing
vlan trunk native 1
vlan trunk allowed all
Initially, the switch may contain VLANs 1, 10, and 20.
If the administrator subsequently creates VLAN 100:
vlan 100
name NEW_USERS
VLAN 100 becomes eligible to traverse interface 1/1/24 without requiring another vlan trunk allowed command.
This differs from explicitly permitting a fixed VLAN list such as 10,20 , where an additional VLAN would need to be added manually.
There is no requirement to shut down and re-enable the interface merely because a VLAN has been created.
There is also no requirement to configure VLAN 100 as the native VLAN.
For successful end-to-end communication, the VLAN must exist where needed, the connected switching devices must permit it, and the relevant forwarding paths must be operational.
The all command permits the new VLAN; it does not independently guarantee connectivity through the entire network.
Therefore, Option A is correct.
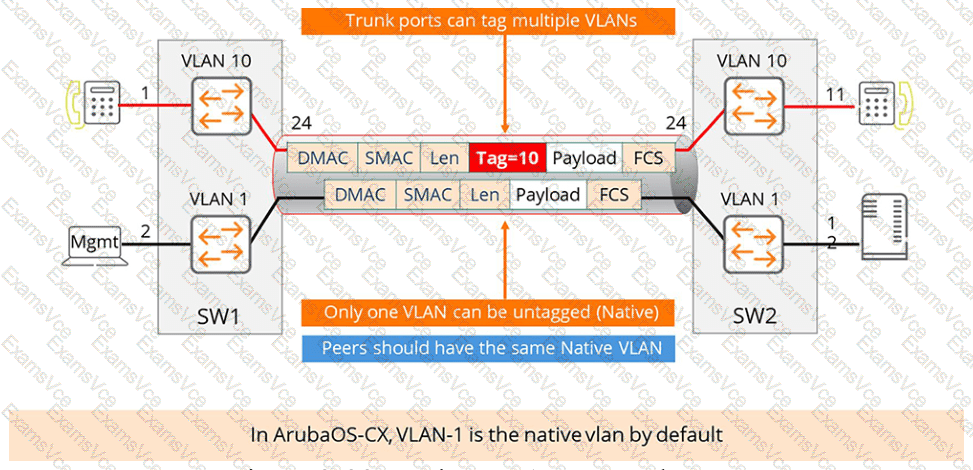
HPE Press study-guide figure / related learning illustration · Q139 Fig 2-33 NativeVLAN



