Pre-Winter Sale Special Limited Time 70% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: xmasmnth

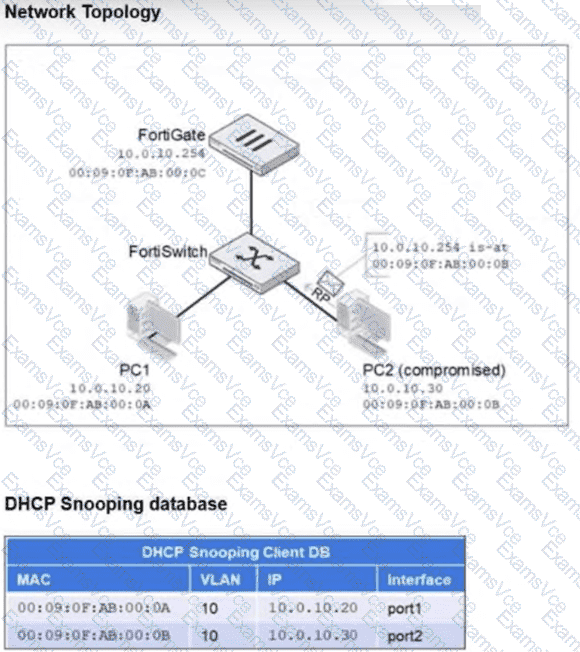
Refer to the exhibits.

Refer to the exhibits.

All three FortiSwitch-connected ports are configured in VLAN 10. FortiGate acts as the Dynamic Host Configuration Protocol (DHCP) server and is connected to a DHCP snooping trusted trunk port. PC1 and PC2 are connected to ports configured as untrusted for Dynamic ARP Inspection (DAI), and no static bindings are configured in the IP source guard (IPSG) database. PC2 is compromised and attempts to spoof the FortiGate IP address by sending forged Address Resolution Protocol (ARP) replies with its own MAC address. What will FortiSwitch do with the ARP packets from PC2? (Choose one answer)

A.

Forward the ARP replies because there are no IPSG bindings blocking them.

B.

Accept the ARP replies because the VLAN has DAI enabled and FortiGate is a trusted DHCP server.

C.

Forward the ARP replies to all VLAN 10 ports because DAI is only active on trusted ports.

D.

Drop the ARP replies because they fail DAI validation against the DHCP snooping database.

Fortinet NSE5_FSW_AD-7.6 Summary

  • Vendor: Fortinet
  • Product: NSE5_FSW_AD-7.6
  • Update on: Sep 15, 2026
  • Questions: 114
Price: $52.5  $149.99
Buy Now NSE5_FSW_AD-7.6 PDF + Testing Engine Pack

Payments We Accept

Your purchase with ExamsVCE is safe and fast. Your products will be available for immediate download after your payment has been received.
The ExamsVCE website is protected by 256-bit SSL from McAfee, the leader in online security.

examsvce payment method