Exact Extract: “The playbook uses a manual trigger, where you can define three mandatory fields: starting destination IP address, ending destination IP address, and user.”
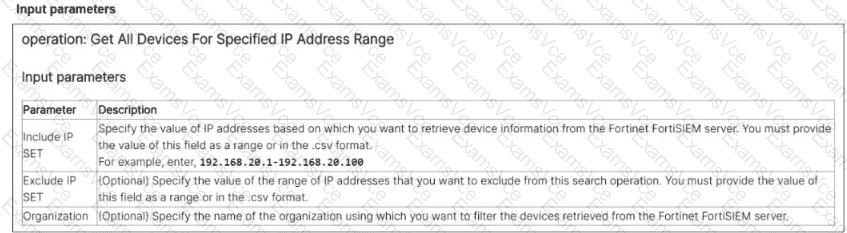
Exact Extract: “This slide shows an example of the Get All Devices For Specified IP Address Range action. This action requires an IP address range as input, with optional parameters to exclude certain IP address ranges and specify a FortiSIEM organization scope.”
Exact Extract: “Record: A record is an entry within any FortiSOAR module. Module: A module is a structured component in the FortiSOAR database. It defines the data structure and behavior for a specific type of record, such as alerts, incidents, or tasks.”
The correct answer is C. The playbook must start with a Manual trigger because the analyst must manually input the IP address range. The next step is the FortiSIEM connector action shown in the exhibit, specifically Get All Devices For Specified IP Address Range, using the manually supplied range as the input parameter. The final step is Create record, targeting the Assets module and mapping each returned device IP address to the asset record fields. This satisfies all requirements with the fewest steps.
Option A is wrong because it has no manual trigger, so there is no proper operator input point for the IP range. Option B is wrong because an On create trigger is event-driven, not manually initiated, and a code snippet is unnecessary for the minimal workflow. Option D works conceptually but is bloated: a Set Variable and Update Record are not required when the connector input and create-record mapping can reference prior step outputs directly.
Technical Deep Dive: In FortiSOAR, the efficient pattern is input → query → record creation. Manual trigger fields become playbook variables. The connector action consumes those variables as the Include IP range. The Create Record step then uses connector output, typically the returned devices.device[] data structure, to create Assets records. This is orchestration-layer automation; FortiGate NP/CP hardware offload is irrelevant because no packet forwarding or content processing is occurring.