Comprehensive and Detailed Explanation
HPE Press guide context | PDF page 588 | HPE Press, Aruba Certified Associate – Campus Access Official Certification Study Guide
Short exact extract: “Aruba Central allows you to manage configurations for different device types.”
Technical Deep Dive — Original Chat Wording
Role-Based Access Control (RBAC) is a security mechanism that associates administrative permissions with defined user roles.
HPE Aruba Networking Central uses RBAC to ensure administrators receive access appropriate to their responsibilities.
The View Only role is intended for personnel who need operational visibility without the ability to change network settings.
For example, monitoring personnel may need to review device availability, network-health dashboards, alerts, and reports while investigating service problems.
Providing read-only permissions allows these users to observe the environment without introducing unnecessary configuration risks.
This supports the principle of least privilege.
A View Only user can inspect permitted dashboards, reports, and analytics but does not receive the same capabilities as an administrator.
Applying network configuration changes requires appropriate write permissions.
Creating new reports and scheduling report generation also generally require report-management permissions beyond read-only access.
Editing dashboards, reports, or analytics configuration similarly requires an authorized management role.
Read-only privileges should not be confused with unrestricted access to every resource. Additional scope restrictions can determine which sites and devices a user is permitted to view.
Therefore, Option B (View dashboards, reports, and analytics) is correct.
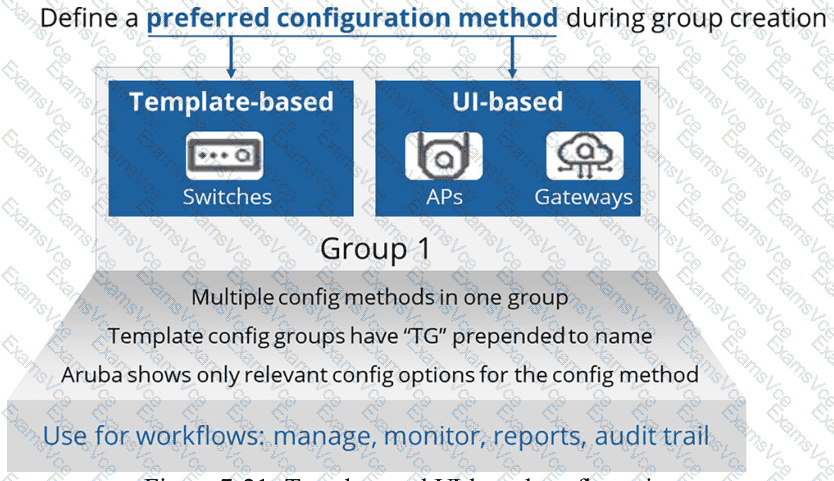
HPE Press study-guide figure / related learning illustration · Q152 Fig 7-21 Groups



